Analysis of the TukTuk C2 Framework and EDR Neutralization Research Linked to The Gentlemen
By Threat Intelligence Unit
Incident Overview
Oasis Security analyzed a server linked to The Gentlemen ransomware operation and identified an environment used to store attack tools, detection evasion research, and data assessed as exfiltrated from global organizations.
The server contained the complete TukTuk C2 development project, DLL sideloading materials, EDR-neutralization tools, vulnerable-driver research, and credentials and infrastructure information associated with technology and healthcare organizations.
Attribution
The strongest attribution artifact was eb.sys, whose SHA-256 hash matched a publicly documented GentleKiller sample associated with The Gentlemen. The server also contained a DLL sideloading package consisting of the legitimate Greenshot.exe executable and a malicious log4net.dll, consistent with techniques previously reported in The Gentlemen intrusions.
Key Findings
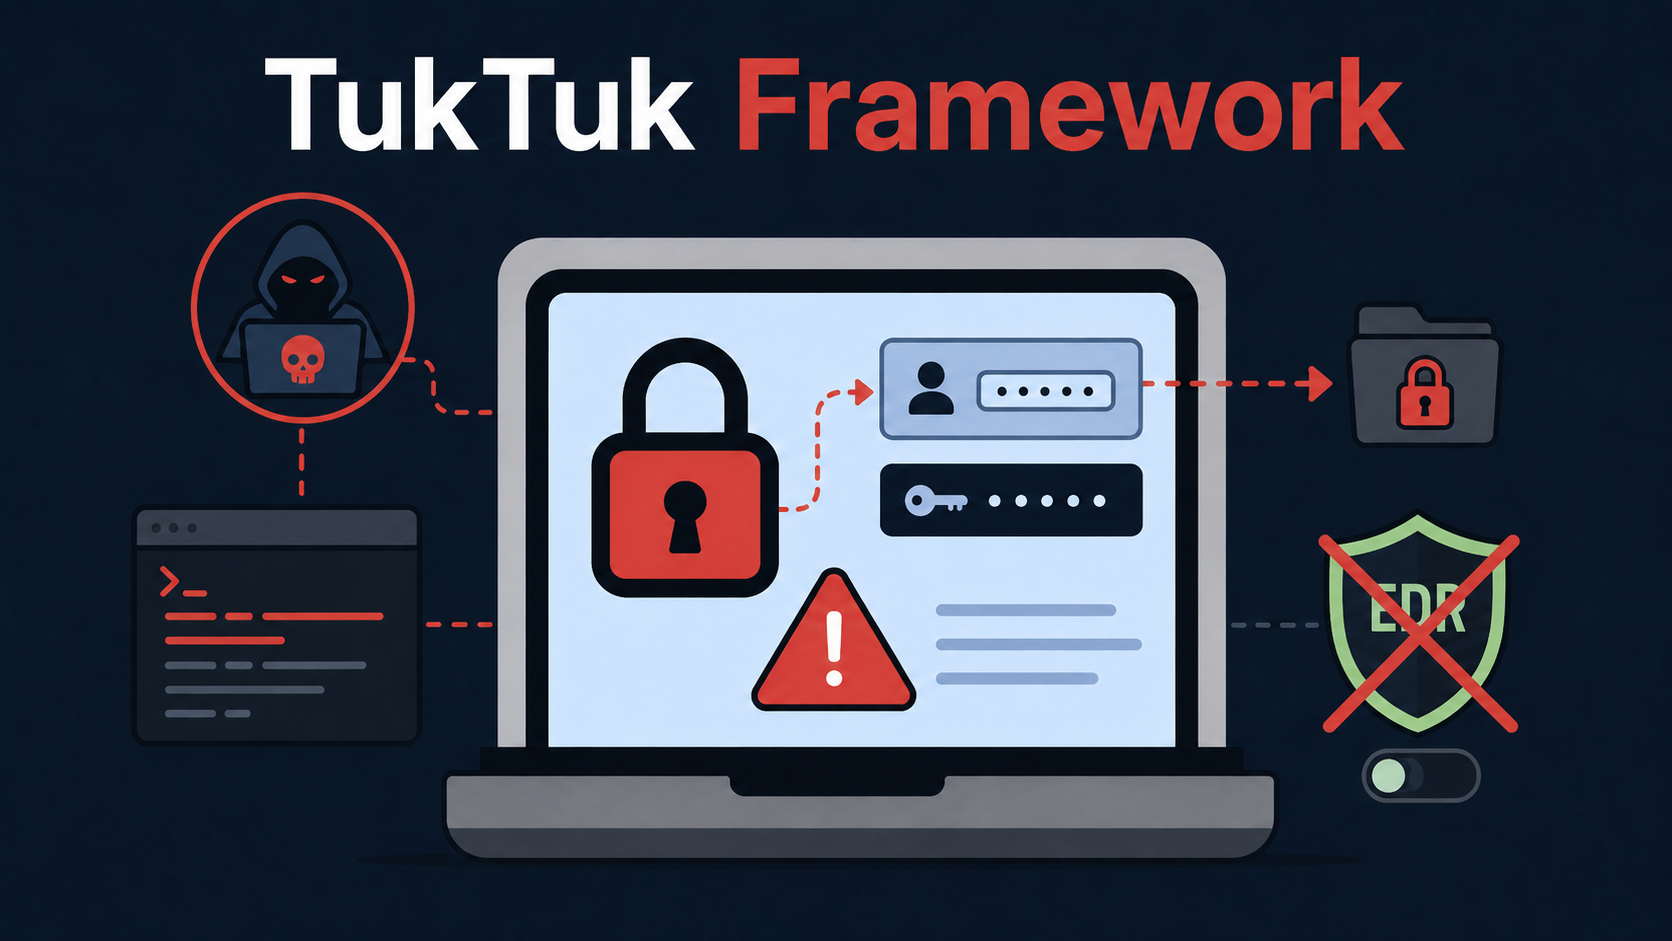
The TukTuk C2 project included a Windows agent, Linux agent, backend service, and operator panel. Its capabilities included host information collection, command execution, file management, screenshot capture, interactive shell activity, and credential theft through a spoofed Windows Security prompt.
The server also contained four training lessons covering EDR-killer development, Bring Your Own Vulnerable Driver (BYOVD) testing, vulnerable-driver hunting, and kernel-level research. Some materials examined how quickly EDR products recovered after process termination, potentially allowing operators to identify a window for follow-on activity.
Impact
The server contained 224 Jira tickets and eight attachments assessed as exfiltrated from a global technology company. Some records included technical information associated with U.S. defense, defense-industry, and aerospace customers.
Separately, credentials and infrastructure information associated with a global healthcare company's Infrastructure-as-Code platform were identified, including information related to cloud services, production databases, directory services, and source code repositories.
The combination of cross-platform C2 development, credential harvesting, EDR neutralization, and data exfiltration indicates that The Gentlemen maintained capabilities extending beyond ransomware deployment alone.