AI in the Hands of Attackers,we use AI to track their infrastructure
OASIS SECURITY uses AI to track attacker C2 servers and the dark web around the clock. Catch attacks while they are still being staged, from the tools and logs attackers leave behind.
Live Demo
Look inside attacker infrastructure yourself
These are the actual product consoles. Browse, menu by menu, what our products collect from attacker infrastructure and the dark web, or hand the whole investigation to AI Insights.
Pick a menu to see what it does
Click a menu in the sidebar
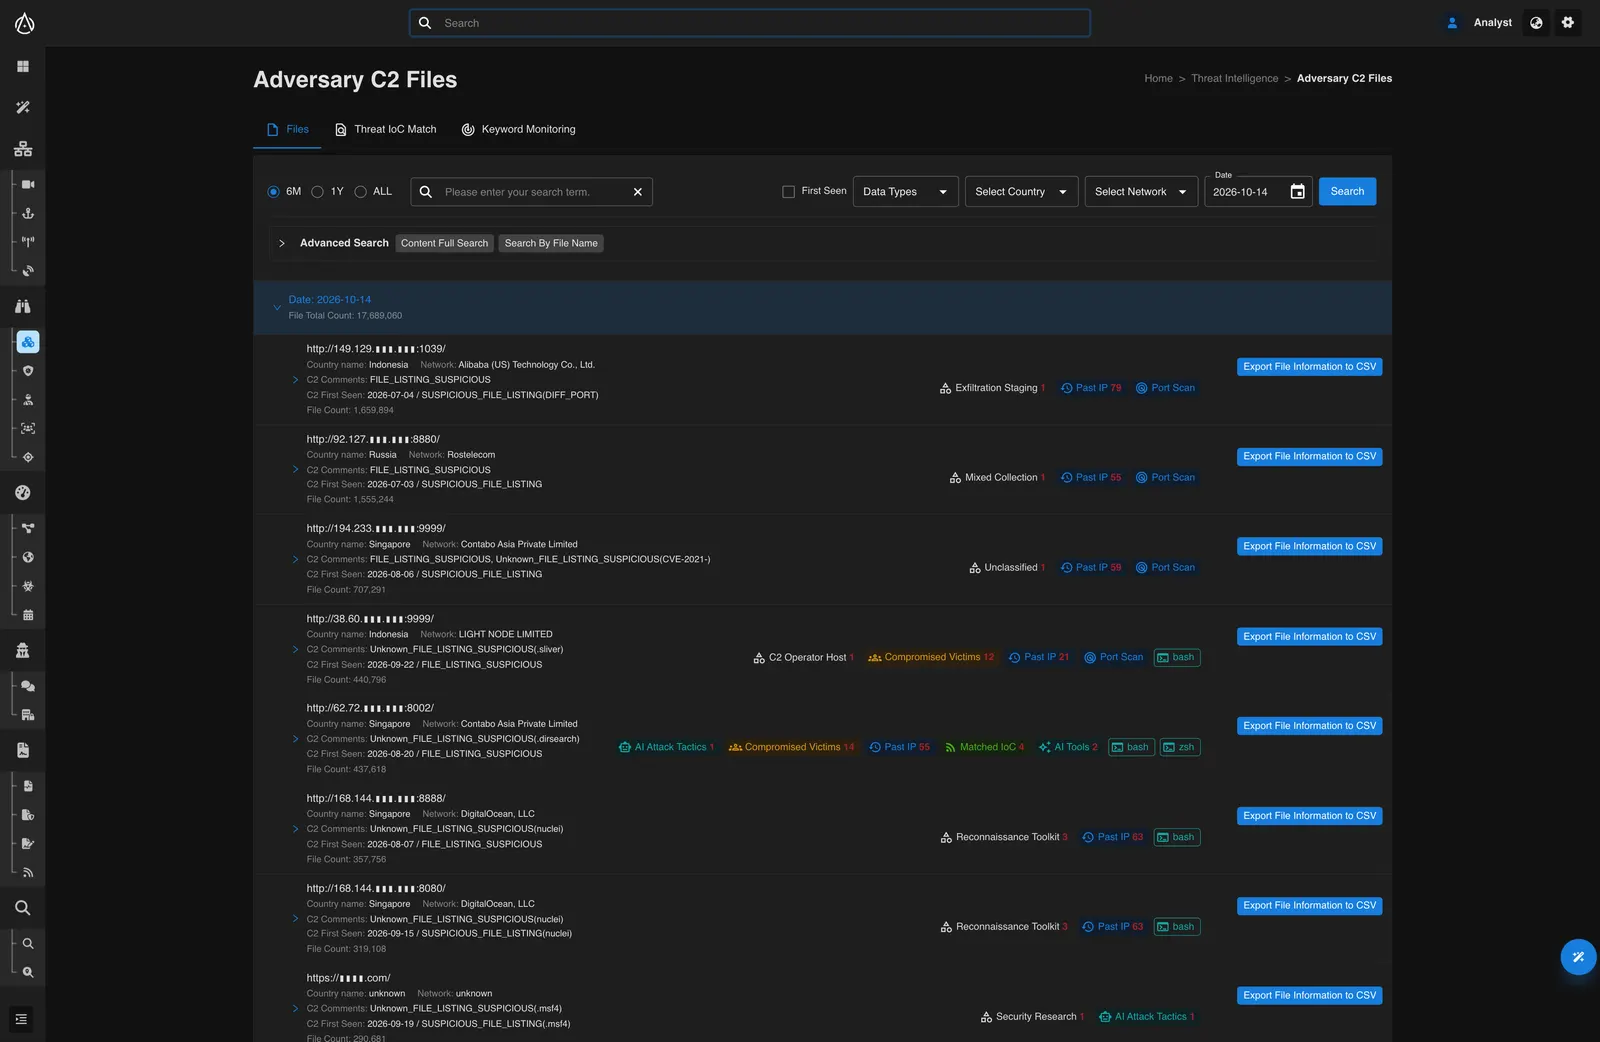
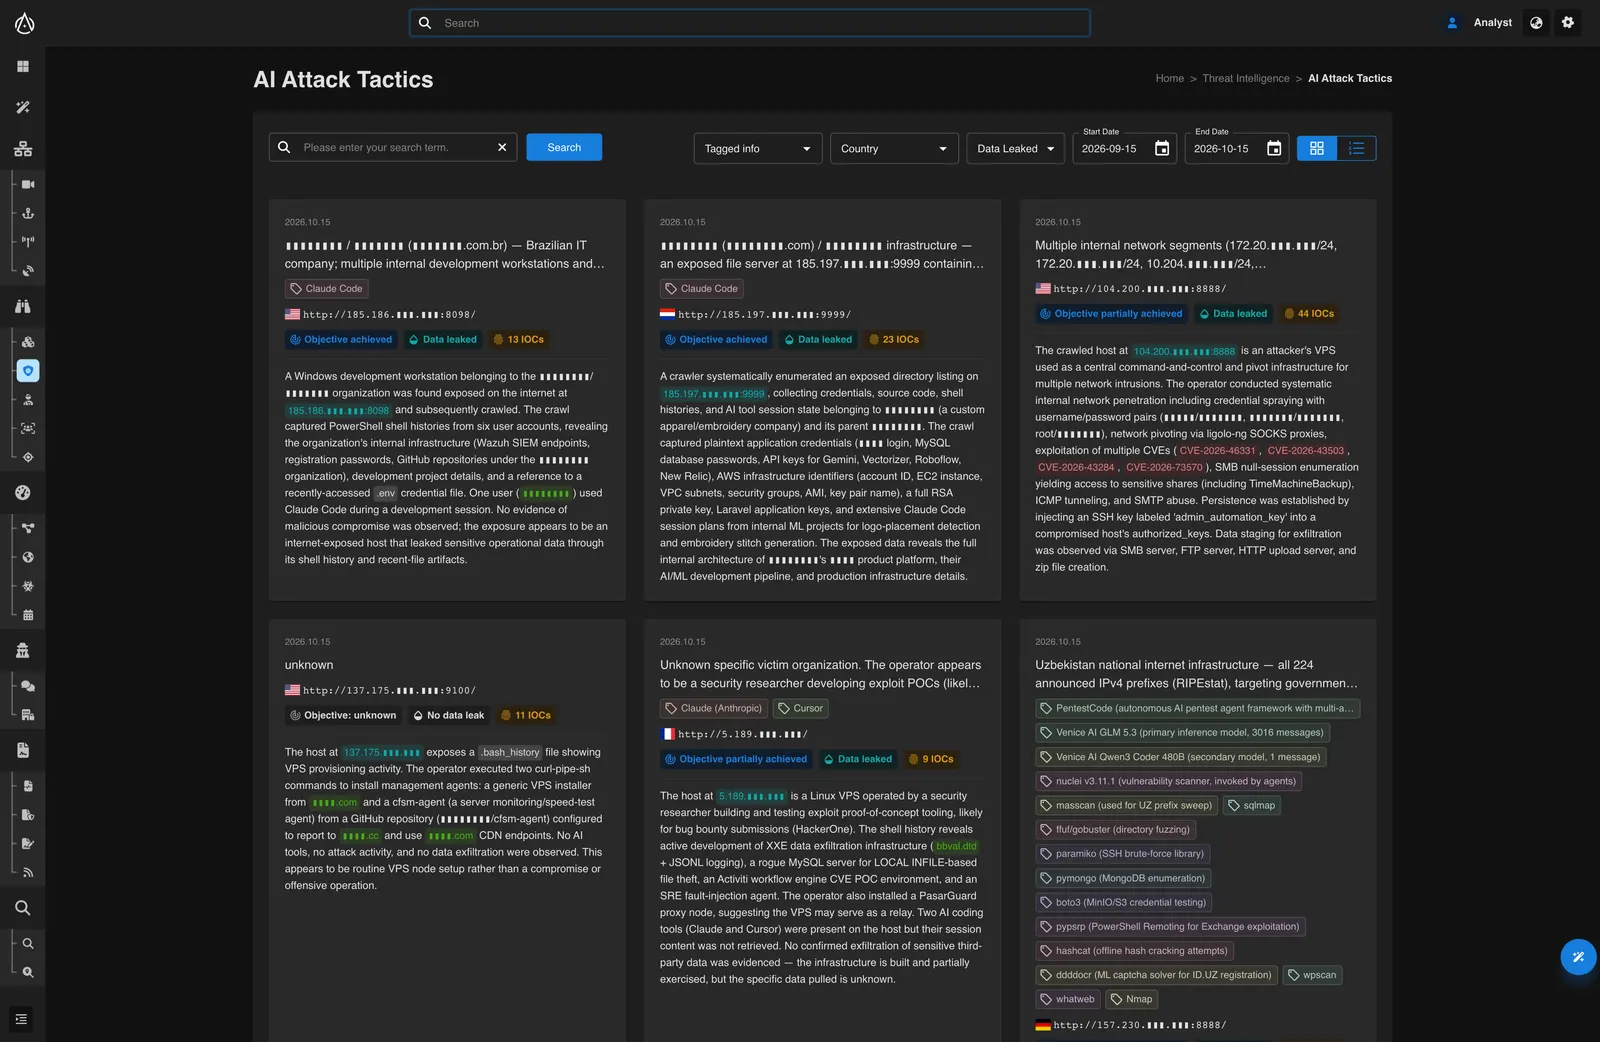
Real product screens · sample data
That's a lot of menus to learn.
Skip the menus. Ask in plain language and AI Insights picks the tools, digs through the data, and writes up what it found.
14,000+ live C2 servers · 390,000+ bad IPs under watch
AI Threat Research
Attackers use AI too
Real cases we confirmed from logs and tools collected directly from attacker servers.
Mass exploitation of exposed LocalAI
A campaign against 243 unauthenticated LocalAI instances. Root-level command execution was confirmed on 23 servers, and data was taken from a workstation tied to the Thai military.
Evidence · Attacker-server tools and callback logs
Read the reportClaude-associated attacks on Brazilian organizations
Recovered Claude-associated sessions expose the workflow end to end: reconnaissance, credential discovery, JWT forgery, and webhook manipulation.
Evidence · Recovered AI-session logs and attacker-side files
Read the reportHephaestus: a Claude-powered attack framework
A framework automating everything from reconnaissance to persistence and reporting, used against government and academic targets in Indonesia, Bangladesh, Thailand, and South Korea.
Evidence · Operational artifacts from the framework
Read the reportJailbroken Claude in attacks on Mexican government targets
The attacker used a jailbroken Claude for reconnaissance, SQL injection, credential stuffing, and lateral movement, and exfiltrated roughly 150 GB of data.
Evidence · Jailbreak logs from the attacker's server
Read the reportThe Attacker's View
Every stage of an attack, seen from the attacker's side
Log- and endpoint-based detection starts once an attack reaches your network. OASIS SECURITY starts on the attacker's infrastructure, while the attack is still being built.
- 01
Infrastructure staging
Attacker
Domains are registered and C2 servers are deployed.
AGATHA tracks C2 domain registrations by date and catches C2 frameworks the moment they activate.
- 02
Reconnaissance
Attacker
Scanners and AI agents hunt for targets and probe them for weaknesses.
AGATHA collects the scan results, target lists, and AI recon logs left on attacker servers, so you see who is being targeted first.
- 03
Tool deployment
Attacker
Attack frameworks like Cobalt Strike and Sliver are deployed alongside exploits.
AGATHA pulls tool and config files from attacker servers, recovers beacon configs, and pivots from each tool to the live servers behind it.
- 04
Compromise
Attacker
Attackers breach victim hosts and exfiltrate critical data.
AGATHA traces victims back from the C2: hosts reached, successful attempts, and how much data was taken.
- 05
Monetization
Attacker
Exfiltrated data and access are sold on the dark web.
ARTHUR continuously collects dark web forums, Telegram channels, and ransomware leak sites.
AI Insights connects all five stages. One question takes you from attacker infrastructure to the victims and where the data went.
Products
Two products, live today
Both run on the same AI collection and analysis engine.
AGATHA
LiveTrack attacker infrastructure before it's weaponized
AGATHA detects C2 servers, phishing kits, and compromised hosts while they are still being staged, giving your organization time to neutralize threats before attacks launch.
- Follow C2 frameworks like Cobalt Strike and Sliver as servers go live
- Filter global C2 infrastructure by country, network, and tooling
- Query up to 3,000 IPs, domains, and hashes in a single bulk search
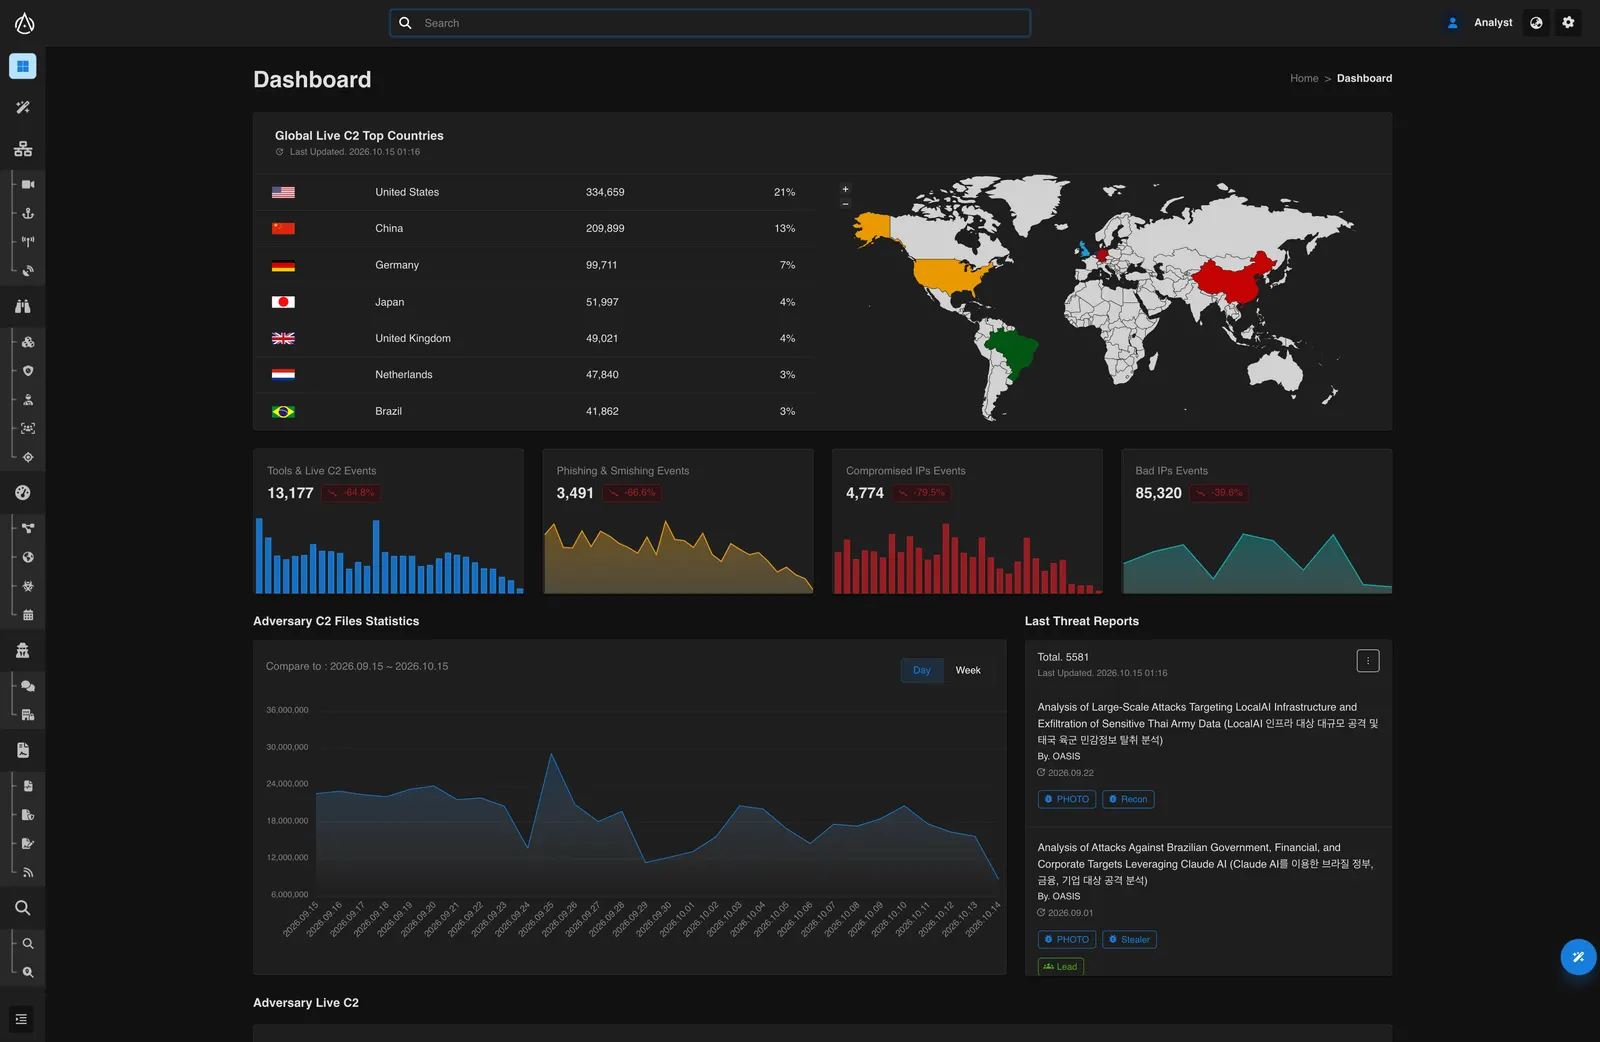
ARTHUR
LiveDeep and dark web intelligence, continuously collected
ARTHUR continuously monitors hidden marketplaces, illicit forums, and threat actor chatter to surface leaked assets and emerging campaigns before they materialize inside your perimeter.
- 82 Telegram threat channels and 42 dark web forums, crawled continuously
- 143 ransomware leak sites tracked as victim posts appear
- 4.4M+ cryptocurrency addresses collected from the deep and dark web
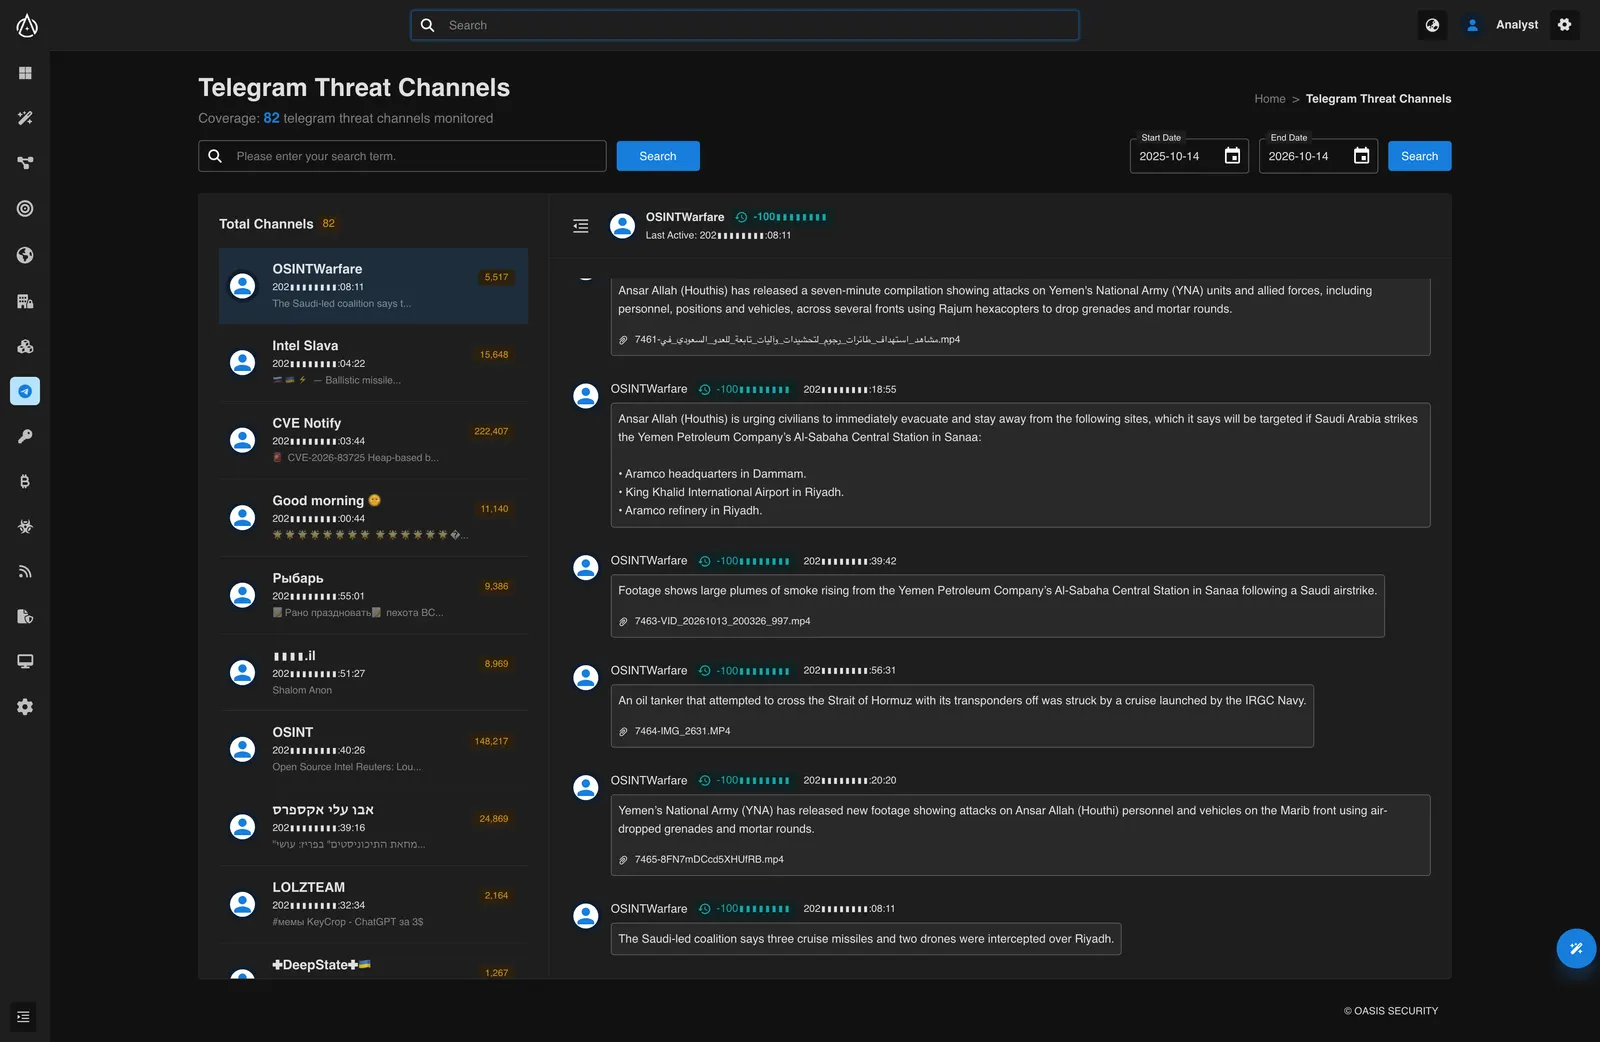
DASHIELL
Coming SoonDASHIELL maps and monitors your attack surface, predicting where you are most likely to be hit, so you can close exposures before attackers find them.
See it on your own attack surface
Book a live walkthrough of AGATHA and ARTHUR with our team, or talk to us about partnering.